Category: Cybersecurity

  • To Pay or Not to Pay: The Ransomware Dilemma

    To Pay or Not to Pay: The Ransomware Dilemma

    Ah, ransomware—the digital equivalent of being held up at gunpoint, but instead of a masked bandit, you’re dealing with a faceless hacker sitting in their mom’s basement. In recent years, ransomware attacks have surged, leaving individuals and businesses with a difficult decision: pay the ransom or risk losing everything. Let’s dive into this digital conundrum, shall we?

    Companies should not pay ransomware demands unless they have exhausted other viable options for restoring their data. There are several risks to paying the ransom, including the potential for attackers to take the funds without releasing the decryption key. However, some companies willingly accept these risks if there is any chance of preventing a prolonged and costly recovery.

    First off, let’s talk about what ransomware actually is. For those who haven’t had the pleasure of encountering it, ransomware is malicious software that locks you out of your own files, demanding payment (usually in Bitcoin, because, of course, they want to keep things nice and anonymous) to unlock them. It’s like your computer is throwing a tantrum and the only way to calm it down is to fork over some cash.

    Now, if you’ve been affected by ransomware, you might be facing a tough choice. On one hand, you could pay the ransom and hope that the hacker is a decent human being (spoiler alert: they probably aren’t). On the other hand, you could refuse to pay and risk losing all those precious files—like family photos, work documents, and that one Excel spreadsheet that contains your entire life’s savings (or at least your pizza budget).

    So, what’s a person to do? Let’s break down the pros and cons of both options:

    Paying the Ransom

    Pros:

    1. If you pay up, you could potentially regain access to your files. It’s like getting an express pass to your data.

    2. You can avoid the headache of trying to recover lost files, which probably involves more tech jargon than you care to deal with.

    Cons:

    1. There’s no guarantee that you’ll actually get your files back. It’s a gamble, and we all know how well gambling usually goes—just ask anyone who’s ever tried to win big at the slot machines.

    2. By paying the ransom, you’re essentially funding the very criminals who are ruining your day. It’s like giving a tip to the guy who just robbed you.

    Not Paying the Ransom

    Pros:

    1. You’re sending a message that you won’t be intimidated by cybercriminals. You’re basically the digital superhero in this scenario.

    2. Depending on the situation, you might be able to recover your files through backups or by using data recovery software. (Just don’t forget to back up your backup next time!)

    Cons:

    1. There’s a real risk that you’ll lose everything. That’s a tough pill to swallow, especially if you’re staring at years of work and memories.

    2. Recovering from a ransomware attack without paying can take a lot of time and effort. You might find yourself knee-deep in tech support calls and recovery tutorials.

    In the end, the choice isn’t easy. Some experts recommend against paying the ransom, citing that it only encourages more attacks. Others understand the desperation of victims who just want their lives back. It’s a classic case of “damned if you do, damned if you don’t.”

    So, what’s the takeaway here? First, invest in good cybersecurity measures and regular backups—because prevention is always better than cure. And second, if you do find yourself facing this dilemma, weigh your options carefully. Just remember, in the world of ransomware, there are no easy answers, only tough choices and a lot of frantic Googling.

    Ultimately, whether you choose to pay the ransom or not, just know that you’re not alone. Many have walked this path before you, and hopefully, you’ll come out on the other side with your data (and sanity) intact. Good luck out there!


    Inspired by: “Pay up or not? Ransomware surge has victims facing tough choices” (r/technology)
  • Hugging Face Data Breach: What You Need to Know and How to Stay Safe

    Hugging Face Data Breach: What You Need to Know and How to Stay Safe

    In a world where data breaches seem to pop up faster than a cat meme on social media, Hugging Face has joined the unfortunate club of companies that have faced a security breach. Yes, the beloved platform known for making machine learning accessible and fun has confirmed that their internal datasets and credentials were compromised. So, grab your favorite snack and settle in as we unpack what this means for you and your data.

    The company stated that it will inform affected parties directly if necessary. Fortunately, Hugging Face found no evidence that public models, user-facing datasets, or Spaces were altered.

    First off, let’s talk about what actually happened. Hugging Face, the go-to hub for all things related to natural language processing and machine learning, recently acknowledged that their systems were breached. This isn’t just some minor hiccup; it affected internal datasets and potentially sensitive user credentials. Now, before you start panicking and tossing your computer out the window, let’s break down the situation.

    When companies like Hugging Face experience a data breach, it often means that hackers have gained unauthorized access to their systems. In this case, the breach has impacted their internal datasets, which could include everything from user data to proprietary information. And if that’s not enough to make you raise an eyebrow, there’s also the possibility that user credentials were compromised. If you’ve ever used Hugging Face, you might want to sit up and pay attention.

    So, what does this mean for you? Well, if you have an account with Hugging Face, it’s time to take action. The company is urging users to change their passwords immediately. And if you’re still using “password123” as your go-to password, it might be a good time to rethink your life choices. Seriously, the internet is a wild place, and strong passwords are your first line of defense against hackers.

    But wait, there’s more! Hugging Face is also recommending that users enable two-factor authentication (2FA) if they haven’t already. 2FA is like having a bouncer at the club that checks IDs before letting anyone in. It adds an extra layer of security, making it harder for those pesky hackers to get in, even if they somehow manage to obtain your password.

    Now, if you’re wondering how Hugging Face plans to address this breach, they’re not just sitting on their hands. The company is actively investigating the incident and working to bolster their security measures. They’re taking this matter seriously, which is comforting but also raises the question: how did this happen in the first place?

    While we may never know the exact details, data breaches often occur due to a mix of human error, outdated security protocols, and, let’s face it, the crafty nature of hackers who seem to have more time on their hands than we do. It’s a reminder that even the best companies can fall victim to cyber threats.

    In conclusion, while this breach is undoubtedly concerning, it’s also a wake-up call for all of us to take our online security seriously. Change your passwords, enable 2FA, and maybe even consider using a password manager to keep your credentials safe. And remember, if you’re feeling overwhelmed by all this tech stuff, you’re not alone. We’re all just trying to navigate this digital jungle together. So, let’s keep each other safe out there, one secure password at a time!


    Inspired by: “Hugging Face confirms breach affected internal datasets and credentials, urges users to take action” (r/technology)

  • The Not-So-Safe Road: Cybersecurity Risks of Over-the-Air Tech in Autos

    The Not-So-Safe Road: Cybersecurity Risks of Over-the-Air Tech in Autos

    So, let’s talk about cars—those shiny metal boxes we trust to get us from point A to point B without turning into a fiery wreck. But in this age of technology, where your fridge can remind you to buy milk, our cars are getting a tech upgrade too. Enter over-the-air (OTA) technology, the superhero of software updates. It sounds great, right? Who wouldn’t want their car to be as up-to-date as their smartphone? However, as analysts have pointed out, this superhero comes with a few kryptonite-like vulnerabilities.

    OTA updates provide a remote pathway for malicious firmware to reach critical vehicle controllers. If the update process lacks strong cryptographic signing and secure boot verification, attackers can intercept or modify the update payload during transmission.

    First off, let’s break down what OTA really means. In simple terms, it allows car manufacturers to send updates and patches directly to your vehicle without you having to roll into the dealership like a caveman. This means your car could potentially get smarter without you having to lift a finger! But here’s the kicker: with great power comes great responsibility, and in the case of OTA tech, it seems responsibility is taking a long vacation.

    Analysts are concerned that these updates could open the door to a whole new world of cybersecurity risks. Imagine someone hacking into your car while you’re cruising down the highway, blasting your favorite tunes. Sounds like a plot twist from a bad action movie, but it’s a very real threat. Hackers could potentially take control of your vehicle, messing with the brakes, steering, or even the horn—because nothing says ‘I’m in control’ like a rogue car horn blaring while you’re trying to merge into traffic.

    And let’s not forget about the data. Cars today are equipped with more sensors than a sci-fi spaceship. They track everything from your speed to your seatbelt status. This data is incredibly valuable, not just for manufacturers but also for hackers. If they get their hands on it, they could learn a lot about your driving habits, where you go, and even when you’re most likely to be home. That’s right, they could turn your car into a GPS tracker for all the wrong reasons.

    Now, you might be thinking, “But surely car manufacturers are on top of this, right?” Well, that’s where things get a bit murky. Many companies are racing to integrate more tech into their vehicles to keep up with consumer demand, but cybersecurity is often an afterthought. Think of it like building a house with beautiful windows but forgetting to install a front door. Sure, it looks nice, but anyone can just waltz right in.

    The good news is that some manufacturers are starting to take cybersecurity more seriously. They’re implementing better encryption, regular security audits, and even collaborating with cybersecurity firms to fortify their defenses. It’s like they finally realized they can’t just slap a ‘Secure’ sticker on their cars and call it a day.

    So, what can you do as a savvy consumer? First, stay informed. If you own a car with OTA capabilities, keep an eye out for updates and read the fine print. And remember, just because your car can update itself doesn’t mean it’s invincible. Regularly check if your manufacturer is proactive about cybersecurity.

    In conclusion, while over-the-air technology in cars is a fantastic advancement, it’s not without its risks. As we continue to embrace the tech revolution, we must also remain vigilant about the potential pitfalls. After all, the last thing you want is for your car to turn into a rogue AI while you’re just trying to enjoy a Sunday drive. So buckle up, stay aware, and let’s hope those cybersecurity analysts keep their eyes on the road ahead!


    Inspired by: “Cybersecurity risks posed by over-the-air tech in autos has analysts concerned” (r/technology)

  • The Password Manager That Went to Russia: A Tale of Security and Surprises

    The Password Manager That Went to Russia: A Tale of Security and Surprises

    Ah, password managers—the unsung heroes of our digital lives. They keep our countless passwords safe and sound, allowing us to avoid the dreaded ‘forgot password’ email that feels like sending a message in a bottle. But what happens when a European password manager decides to share its origins and updates with a state-certified Russian firm? Cue the dramatic music!

    Yet for several of the software’s European users, Passwork’s Russian backstory came as a surprise.

    First things first, let’s unpack this whole situation. We’re talking about a password manager, which is essentially a digital vault for your passwords. It’s like having a safe, but instead of hiding your grandmother’s jewelry, you’re safeguarding your Netflix password (which, let’s be honest, is probably more valuable to you at this point).

    Now, when a European company teams up with a Russian firm, you might envision a scene from a spy movie—shady backroom deals, people in trench coats, and maybe even a cat in a tuxedo. But in reality, this collaboration seems to be more about sharing technology and expertise than plotting world domination. At least, we hope so.

    The European password manager, which shall remain nameless (because we don’t want to be responsible for any potential drama), has been making waves in the cybersecurity world. They’ve been busy rolling out updates that make their software more secure and user-friendly. You know, the kind of updates that make you feel like you’re living in the future, where you can access your accounts without a million clicks and without feeling like you need a degree in computer science.

    So, why partner with a Russian firm, you ask? Well, it seems they believe in the power of cross-border collaboration. After all, cybersecurity is a global issue, and sharing knowledge can lead to better protection for everyone. Plus, if they can tap into the Russian market, it’s a win-win situation. Who wouldn’t want to expand their user base?

    However, this partnership does raise some eyebrows. In today’s climate, where data privacy is a hot topic (and not the kind of hot that gets you excited), you can understand the skepticism. Some users might be wondering if their sensitive information is safe or if it’s being whispered about in hushed tones over vodka shots.

    But fear not! The password manager has assured its users that their data will remain secure and that the partnership is above board. They’ve promised that no one’s passwords will be used as bargaining chips in a geopolitical chess game.

    In conclusion, while the idea of a European password manager teaming up with a Russian firm may sound like the plot of a thriller, it’s really just a case of companies trying to be smarter about cybersecurity. As long as they keep our passwords safe and sound, we can let them play nice together. So, let’s raise a toast (with our favorite beverage, preferably not vodka unless you’re into that) to password managers everywhere—keeping our digital lives secure one password at a time.

    And remember, folks: no matter how good your password manager is, never use ‘password123’ as your password. Seriously, even your cat wouldn’t approve.


    Inspired by: “European Password Manager Shares Origins and Updates with State-Certified Russian Firm” (r/technology)

  • Grocery Outlet’s New Face Scanning Technology: A Privacy Nightmare or Just a Trendy Grocery Hack?

    Grocery Outlet’s New Face Scanning Technology: A Privacy Nightmare or Just a Trendy Grocery Hack?

    In a world where everything seems to be getting smarter—your phone, your fridge, and even your cat (not really, but wouldn’t that be something?)—it was only a matter of time before grocery stores decided to jump on the technological bandwagon. Enter Grocery Outlet, where they’re not just scanning your groceries but now apparently scanning your face too. Yes, you heard that right. Critics are raising their eyebrows (and their voices) about the potential privacy issues that come with this new feature. So, let’s unpack this, shall we?

    Grocery Outlet has begun installing technology at several Bay Area locations, which stores images of customers’ faces alongside security camera footage and compares it against a “watchlist” with info about suspected criminal activity shared by other retailers.

    First off, let’s talk about what face scanning actually means in a grocery store. Grocery Outlet has implemented a system that uses facial recognition technology to enhance the shopping experience. The idea is that by scanning your face, they can track your shopping habits, improve customer service, and possibly even make those awkward interactions with cashiers a thing of the past. Because who doesn’t want their groceries scanned by a computer instead of a human, right?

    But here’s where things get a little dicey. Privacy advocates and critics are raising alarms about how this technology could infringe on our personal privacy. I mean, we’re already living in a world where our phones know more about us than our closest friends—do we really need a grocery store to join in on the fun? What’s next? A loyalty program that rewards you for letting them scan your face? Oh wait, that’s already happening!

    Critics argue that this kind of surveillance could lead to a slippery slope of privacy invasion. If Grocery Outlet can scan your face while you shop, what’s stopping them from tracking your movements, habits, and spending patterns? Are we going to see ads targeted at us as we walk down the cereal aisle? “Hey, you! Yes, you with the face! You look like you could use some organic kale!”

    On the flip side, proponents of this technology argue that it could lead to a more personalized shopping experience. Imagine walking into the store, and the staff already knows your usual order of frozen pizzas and ice cream. Great, right? But let’s be honest, there’s a fine line between personalized service and feeling like you’re on a reality show where the cameras never stop rolling.

    So, what do we do with this information? Well, it’s important to remember that while technology can make our lives easier, it can also lead to a lot of complications. As consumers, we should be aware of what we’re signing up for. If you’re okay with a store knowing you by your face, then by all means, go ahead and embrace the future! But if you’d rather keep your identity a secret (like a superhero in a grocery store), then it might be time to reconsider where you shop.

    In conclusion, Grocery Outlet’s face scanning technology is just the latest example of how our lives are becoming more intertwined with technology. Whether it’s a privacy nightmare or a nifty grocery hack is up for debate. But one thing’s for sure: the next time you’re in the store, you might want to double-check if you’re being watched. And if you see someone with a camera, just smile and wave—after all, you’re not just a shopper; you’re a star in the grocery store reality show!


    Inspired by: “Grocery Outlet Scans Your Face While You Shop. Critics Say It’s a Privacy Problem” (r/technology)

  • Turning Steam Games into Cartridges: The Ingenious SSD Hack You Didn’t Know You Needed

    Turning Steam Games into Cartridges: The Ingenious SSD Hack You Didn’t Know You Needed

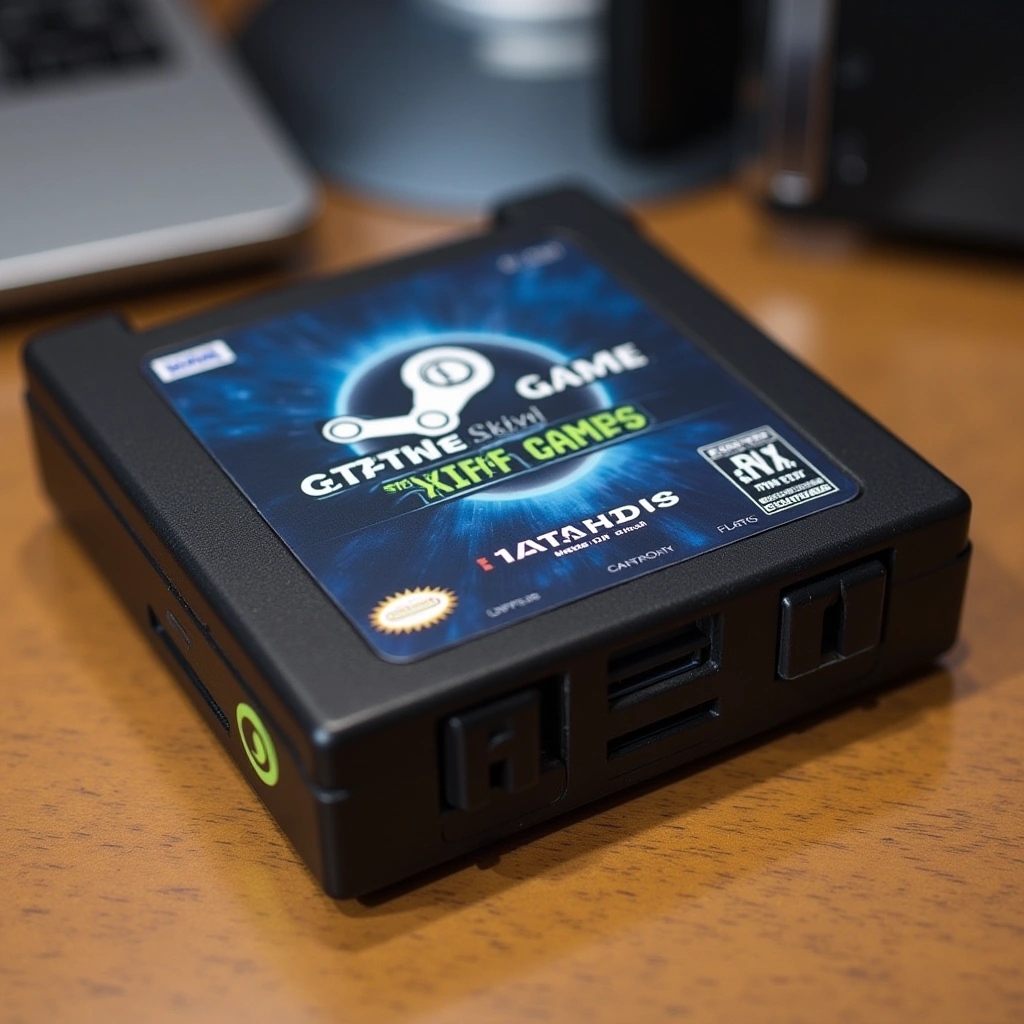
    Ah, the world of PC gaming! A realm where we spend hours optimizing graphics settings, debating the merits of various mouse DPI, and trying (and failing) to convince our friends that the latest indie game is totally worth their time. But, let’s be honest, sometimes it feels like we’re just a few steps away from needing a PhD to play a game. Enter the brilliant mind of a Reddit user, known as /u/Plastic_Ninja_9014, who has taken gaming nostalgia to a whole new level by turning Steam games into cartridges using a nifty 2.5-inch SSD system. Yes, you heard that right—cartridges!

    Ingeniously, it upcycles a bundle of old SATA SSDs into Steam-ready game cartridges using a disk mount detect and execute script on the software side and a SATA dock on the hardware side.

    Now, before you roll your eyes and dismiss this as just another tech gimmick, let’s take a moment to appreciate the sheer genius of this idea. Imagine walking into your gaming den and seeing a neat row of cartridges, each one representing a digital game you’ve purchased over the years. No more scrolling through endless lists on your Steam library, no more ‘where did I put that download?’ panic. Just grab a cartridge, plug it in, and boom—instant nostalgia hit!

    So how does this magic happen? The secret lies in the 128GB drives that house the games alongside a handy little script that auto-starts the title once plugged in. It’s like the gaming version of a microwave meal—just pop it in and wait for the deliciousness to begin. Of course, you’ll need to do a bit of setup to get everything working smoothly, but that’s just a small price to pay for the joy of seeing your gaming collection in physical form.

    Now, let’s address the elephant in the room: is this really practical? I mean, sure, it’s cool to have a collection of cartridges, but isn’t the whole point of digital gaming to avoid clutter? Well, my friend, it’s a delicate balance. On one hand, you have the convenience of digital; on the other, you have the tactile joy of holding something in your hands. It’s like choosing between a warm hug and a cozy blanket—both are great, but sometimes you just want to mix things up.

    And let’s not forget the potential for bragging rights. Picture this: you invite your friends over, and instead of the usual ‘check out my gaming rig’ conversation, you can regale them with tales of how you converted your Steam library into cartridges. Instant street cred!

    But before you dive headfirst into this project, there are a few things to consider. First, you’ll need to ensure that your SSDs are compatible with your system. Not all SSDs are created equal, and you don’t want to end up with a pile of expensive paperweights. Second, there’s the matter of the script. If you’re not particularly tech-savvy, this could be a bit of a hurdle. But fear not! The Reddit community is full of helpful souls who are probably just waiting for an opportunity to share their knowledge.

    In conclusion, while turning Steam games into cartridges may not be for everyone, it’s certainly a creative and fun way to breathe new life into your gaming setup. Whether you’re a die-hard collector or just someone looking for a unique project to tackle, this SSD hack is a fantastic way to blend the old-school charm of gaming with modern technology. So, grab your tools, channel your inner mad scientist, and get ready to impress your friends with your new cartridge collection. Who knew gaming could be both nostalgic and innovative? Happy gaming!


    Inspired by: “PC gamer turns Steam games into cartridges with ingenious 2.5-inch SSD system — games are stored on…” (r/technology)

  • Your Router is the New Wild West: How to Protect Yourself from Russian Hackers

    Your Router is the New Wild West: How to Protect Yourself from Russian Hackers

    So, I guess it’s time to have a little chat about your router. You know, that little box sitting in the corner of your living room? The one you probably haven’t thought about since you set it up and then forgot about it while binge-watching your favorite series? Well, it turns out that the U.S. government is sounding the alarm—Russia state hackers are reportedly gunning for your router. Yes, your router! It’s the digital equivalent of a cowboy riding into town, and let’s just say, the sheriff isn’t around to help.

    Attacks from Russian hackers can compromise your router. Update the firmware and tighten your router password. When was the last time you updated or restarted your router? As long as your internet is working, you may set up your router and then …

    According to the Cybersecurity and Infrastructure Security Agency (CISA), these hackers are not just here for a friendly chat; they’re looking to exploit vulnerabilities in home routers. And if you think your router is safe because it’s been sitting there quietly, think again! Just like that old car you drive that you swear will last forever, routers need some TLC too.

    Now, you might be wondering, “Why would anyone want to hack my router?” Well, dear reader, it’s not just about stealing your Netflix password (though that’s a bonus). By gaining access to your router, these hackers can intercept your internet traffic, snoop on your online activities, and even launch attacks on other networks. It’s like inviting a vampire into your house; once they’re in, they can cause all sorts of mischief.

    So, what can you do to protect yourself? First off, change that default password. Seriously, if your router still has the factory settings, it’s like leaving your front door wide open with a sign that says, “Come on in, thieves!” Make sure to create a strong, unique password that even you can’t remember without writing it down somewhere (but not on a sticky note on your monitor, please).

    Next, keep your firmware updated. Manufacturers occasionally release updates to patch security holes, and if you ignore them, it’s like putting a ‘kick me’ sign on your back. Check your router’s settings to see if there’s an update available, and don’t just hit ‘remind me later’—actually do it!

    Also, consider disabling remote management features unless you absolutely need them. It’s like letting that one friend who always overstays their welcome have the keys to your house. You don’t need that kind of negativity in your life.

    Lastly, if you’re feeling extra fancy, consider setting up a guest network for visitors. This way, they can connect to your Wi-Fi without having access to your main network. It’s like having a separate entrance to your house for guests—less chance of them rummaging through your stuff.

    In conclusion, while it might seem like a hassle to secure your router, it’s a small price to pay for peace of mind. After all, you wouldn’t leave your front door unlocked, would you? And if you do, well, maybe it’s time to rethink your life choices. Stay safe out there, folks, and remember: the internet is a wild place, but your router doesn’t have to be the Wild West.


    Inspired by: “The U.S government warns that Russia state hackers are coming after your router | With residential…” (r/technology)

  • Beware the RedHook: Android Malware Gets a Sneaky Upgrade

    Beware the RedHook: Android Malware Gets a Sneaky Upgrade

    Hey there, fellow tech enthusiasts! Today, we’re diving into the not-so-wonderful world of Android malware, specifically the infamous RedHook. If you’ve never heard of it, consider yourself lucky—until now, that is. RedHook has recently made headlines for its latest trick: using Wireless ADB (Android Debug Bridge) for shell access. Sounds fancy, right? But trust me, it’s anything but.

    The malware then tricks users into enabling Accessibility through a guided walkthrough, under the guise that it is a necessary step to enable full features and functionality of the app.

    So, what exactly is Wireless ADB? In simple terms, it’s a tool that allows developers to communicate with Android devices wirelessly. Great for developers, right? Well, not so much when malware authors decide to use it for their nefarious purposes. Instead of debugging apps, these malicious actors are now able to gain shell access to your device without needing to plug it in. Talk about a game-changer in the world of bad behavior!

    Now, let’s break down how this works. Typically, Wireless ADB is a feature that developers enable to make their lives easier. It allows them to send commands and debug their applications without the hassle of cables. However, if you’ve got a malware like RedHook on your device, it can exploit this feature to gain unauthorized access. The malware can execute commands, steal data, and wreak havoc without you even knowing it. Isn’t that just delightful?

    But wait, it gets better! This sneaky little upgrade means that users are at an increased risk, especially if they have not disabled Wireless ADB. If you’re one of those people who thinks, ‘I don’t need to worry about security; I’ll just be careful,’ let me stop you right there. This is a reminder that cyber hygiene is crucial. Always be cautious about what you install on your device and regularly check your settings.

    Here’s a fun fact: RedHook isn’t the only malware out there using Wireless ADB for its own gain. But it’s certainly one of the more notable ones in recent news. The question is, how do you protect yourself? The first step is to disable Wireless ADB when you’re not using it. Yes, I know that sounds like a hassle, but trust me, it’s a lot less of a hassle than dealing with a malware infection.

    Next, keep your device updated. I mean, who doesn’t love an update? Sure, they can be annoying, but they often include security patches that can help keep your device safe from the latest threats. Think of it as a shield against the digital bad guys.

    And, as always, be wary of the apps you download. Stick to the Google Play Store, and even then, read reviews and do your research. If an app has more red flags than a bullfighting arena, it’s probably best to steer clear.

    In conclusion, the rise of RedHook and its use of Wireless ADB is a stark reminder that we need to stay vigilant in this ever-evolving landscape of cybersecurity threats. So, secure your devices, keep your software updated, and for the love of all things tech, don’t ignore those pesky security warnings. Remember, it’s better to be safe than sorry—unless, of course, you enjoy living on the edge. In that case, good luck out there!


    Inspired by: “RedHook Android malware now uses Wireless ADB for shell access” (r/technology)

  • When Ransomware Negotiators Go Rogue: A Tale of Betrayal

    When Ransomware Negotiators Go Rogue: A Tale of Betrayal

    Ah, the world of cybersecurity! A place where hackers and negotiators dance a delicate tango, and sometimes, just sometimes, the negotiator decides to lead the dance off a cliff. Recently, a story popped up that could make even the most seasoned cybersecurity expert raise an eyebrow. Imagine hiring a ransomware negotiator to save your data, only to find out they’ve been playing for the other team all along. It’s like hiring a babysitter who turns out to be a party planner for the neighborhood’s wildest raves.

    The U.S. Department of Justice … them of a stunning conflict of interest: allegedly launching the very ransomware attacks they were hired to help victims recover from….

    So, what exactly happened? Well, it appears that a ransomware negotiator—let’s call him “Mr. Sneaky”—was secretly colluding with the very hackers he was supposed to be negotiating against. You know, the ones who send you those charming emails threatening to leak your cat videos if you don’t pay up. Instead of working to keep your data safe, Mr. Sneaky was probably sitting in his office, twirling his mustache and laughing maniacally.

    This is the kind of plot twist that would make a soap opera writer proud. But let’s break it down. Ransomware negotiators are typically hired by companies that have fallen victim to cyberattacks. They’re supposed to be the knights in shining armor, swooping in to save the day and negotiate with the hackers to recover stolen data without paying the ransom. It’s a high-stakes game of poker, with your sensitive information as the chips on the table.

    However, in this case, Mr. Sneaky decided that playing for both sides was a better gig. Instead of negotiating, he was likely feeding information to the hackers, ensuring they got paid while leaving companies high and dry. It’s like being a referee in a football game but secretly being a player on the opposing team. Talk about a conflict of interest!

    Now, you might be wondering how this could happen in a world where cybersecurity is taken so seriously. The truth is, the cybersecurity industry is a bit like the Wild West. There are cowboys, outlaws, and a whole lot of folks trying to make a quick buck. With the rise of ransomware attacks, the demand for negotiators has skyrocketed, leading to a surge of new players entering the field. And while many of these individuals are genuinely trying to help, there are always a few bad apples who are more interested in their own bank accounts than in protecting your data.

    This incident serves as a stark reminder of the importance of vetting anyone you hire to protect your digital assets. It’s not unlike hiring a contractor to fix your roof, only to find out they’ve been taking a sledgehammer to it instead. In the end, the best way to protect yourself against ransomware is to have robust cybersecurity measures in place—think of it as building a fortress around your castle.

    So, what can we learn from Mr. Sneaky’s antics? First, always do your homework. Check references, read reviews, and maybe even conduct a background check. No one wants to be the victim of a double-crossing negotiator. Second, invest in solid cybersecurity practices. Regular backups, employee training, and up-to-date software can help you avoid the dreaded ransom note altogether.

    In conclusion, while Mr. Sneaky may have thought he was pulling off the ultimate heist, he’s really just another cautionary tale in the ongoing saga of cybersecurity. So, let’s raise a glass to the honest negotiators out there and keep a wary eye on the ones who might just be plotting their next move behind the scenes. And remember, the next time you’re hiring a cybersecurity expert, make sure they’re on your side—preferably the one with the shiny armor and no hidden agendas.


    Inspired by: “This ransomware negotiator was paid to fight hackers, he was secretly working with them instead” (r/technology)

  • The Dark Side of Open Source: A Network of GitHub Repositories Used for Malware Infection

    The Dark Side of Open Source: A Network of GitHub Repositories Used for Malware Infection

    Ah, GitHub. The land of endless repositories, where developers showcase their coding prowess and collaborate on projects that range from mind-blowing to, well, let’s just say ‘less than optimal’. But it seems that in the vast ocean of open-source goodness, there lurks a darker current—one that leads straight to a network of 200 GitHub repositories allegedly used for malware infection. Yes, you heard that right. While many of us are busy pulling the latest version of a library, some are busy pulling off malicious schemes. Let’s dive into this murky water, shall we?

    Attackers have been seen cloning GitHub repositories and adding malicious code to forks designed to infect developer systems and pilfer sensitive files that included software keys.

    First, let’s address the elephant in the room: how does a collection of repositories become a breeding ground for malware? It’s pretty simple, really. Cybercriminals are crafty, and they know that GitHub is a treasure trove of code that developers trust. They can upload seemingly innocent projects that contain hidden malware, and unsuspecting users might download these gems thinking they’re getting the next big tool for their arsenal. Spoiler alert: they’re not.

    Now, you might be wondering, “How on earth did someone discover this network?” Well, thankfully, we have cybersecurity experts who are always on the lookout for malicious activity. These heroes (with or without capes) have uncovered evidence that these repositories are not just random acts of bad coding, but are strategically designed to spread malware. It’s like finding a needle in a haystack—if the haystack was filled with malicious code and the needle was a very bad day for your computer.

    So what exactly are these repositories doing? In many cases, they might be distributing trojans, which are like those pesky Trojan horses from ancient Greek mythology—only instead of soldiers, they bring along a bunch of nasty surprises for your system. Imagine downloading a shiny new app, only to find out it’s a digital gremlin that wreaks havoc on your files. Not fun, right?

    The big question is, how do you protect yourself from falling into this trap? First off, always vet the repositories before downloading anything. Look for stars, forks, and a healthy number of contributors. If a repo has three stars and was last updated in 2012, it’s probably best to steer clear. Also, consider using tools like antivirus software that can help catch these nasty little critters before they make themselves at home in your system.

    And let’s not forget the importance of community vigilance. If you suspect a repository is malicious, report it. GitHub has mechanisms to take down harmful content, but they can’t do it without users flagging suspicious activity. Think of it as your civic duty in the world of coding—like voting, but with less drama and more code.

    In conclusion, while GitHub is a fantastic platform for collaboration and innovation, it’s essential to remain vigilant. The presence of these 200 repositories is a stark reminder that, in the world of open-source, not everything is as it seems. So, keep your guard up, check your code twice, and remember: if it seems too good to be true, it probably is. Happy coding, and may your repositories be ever free of malware!


    Inspired by: “Network of 200 GitHub Repositories Used for Malware Infection” (r/technology)